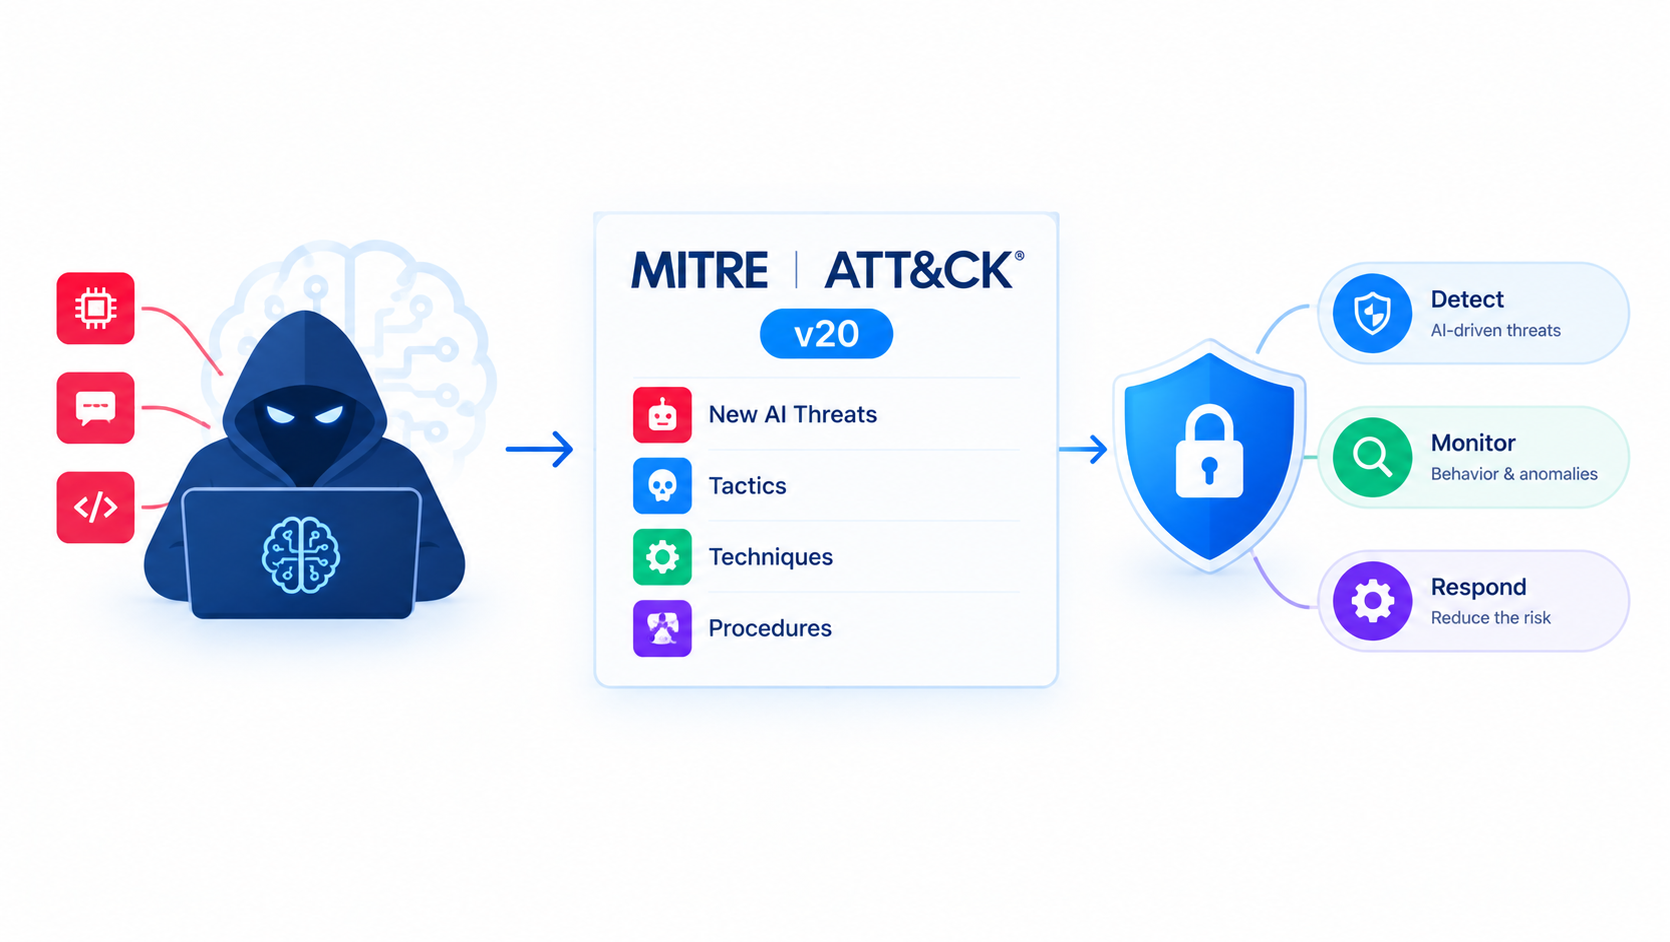
MITRE ATT&CK v20: New AI Threats and How to Defend Against Them
On October 13, 2026, MITRE published version 20 of its ATT&CK framework. Most security teams use ATT&CK to describe attacker behavior and to measure their...
On October 13, 2026, MITRE published version 20 of its ATT&CK framework. Most security teams use ATT&CK to describe attacker behavior and to measure their...
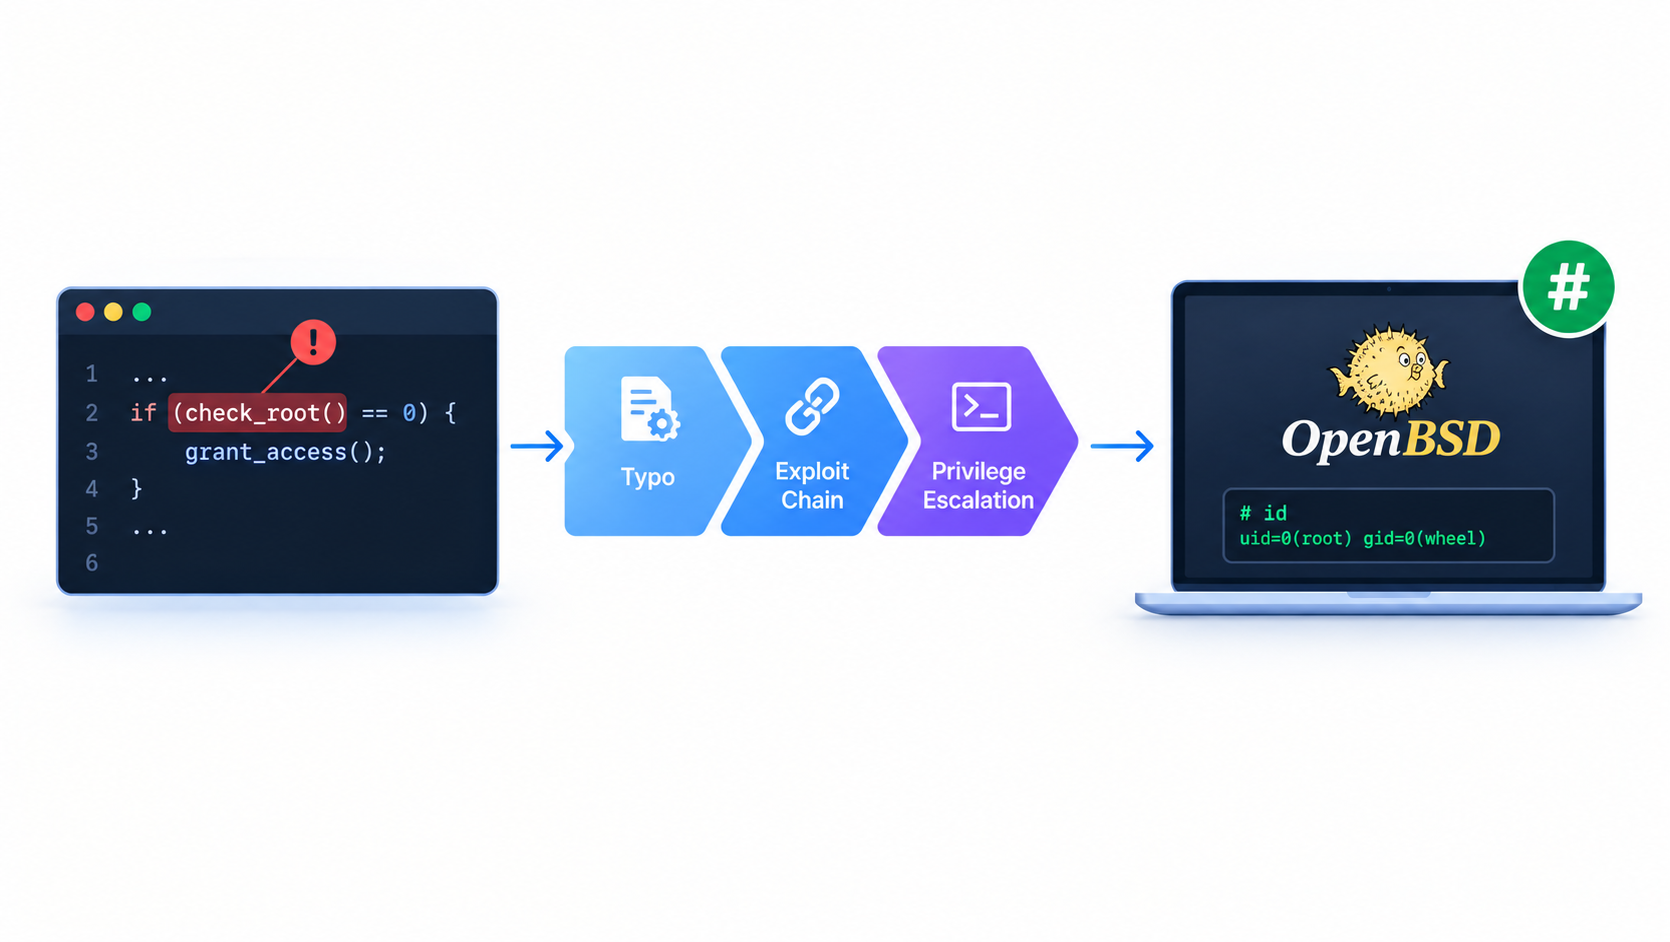
When security researchers at Calif published a working root exploit for OpenBSD 7.9 this week, the most shocking part wasn’t the exploit itself — it...
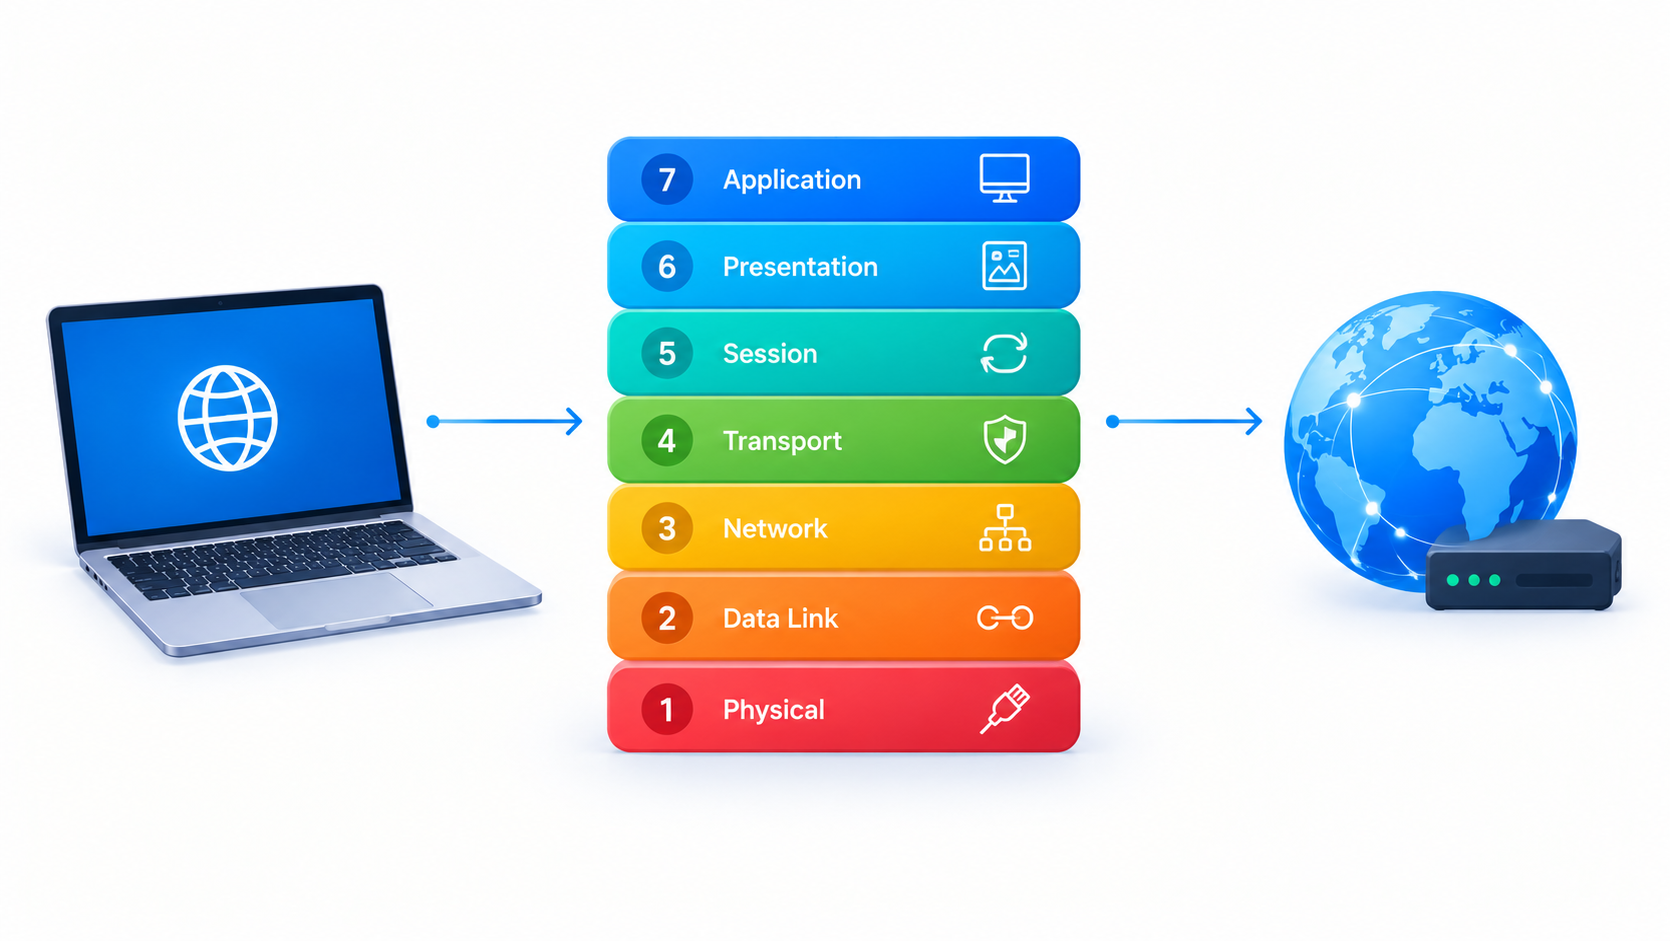
Every time you load a webpage or send a message, your data travels through a complex journey involving cables, routers, switches, and servers. The OSI...
Every few weeks, a new tool claims it can triage alerts, run a pentest, or write an audit report without a human. So I asked...
In August 2026, a persona called CyberLeek began posting unreleased GTA 6 footage. Rockstar’s parent company, Take-Two, then went to court to find the person...
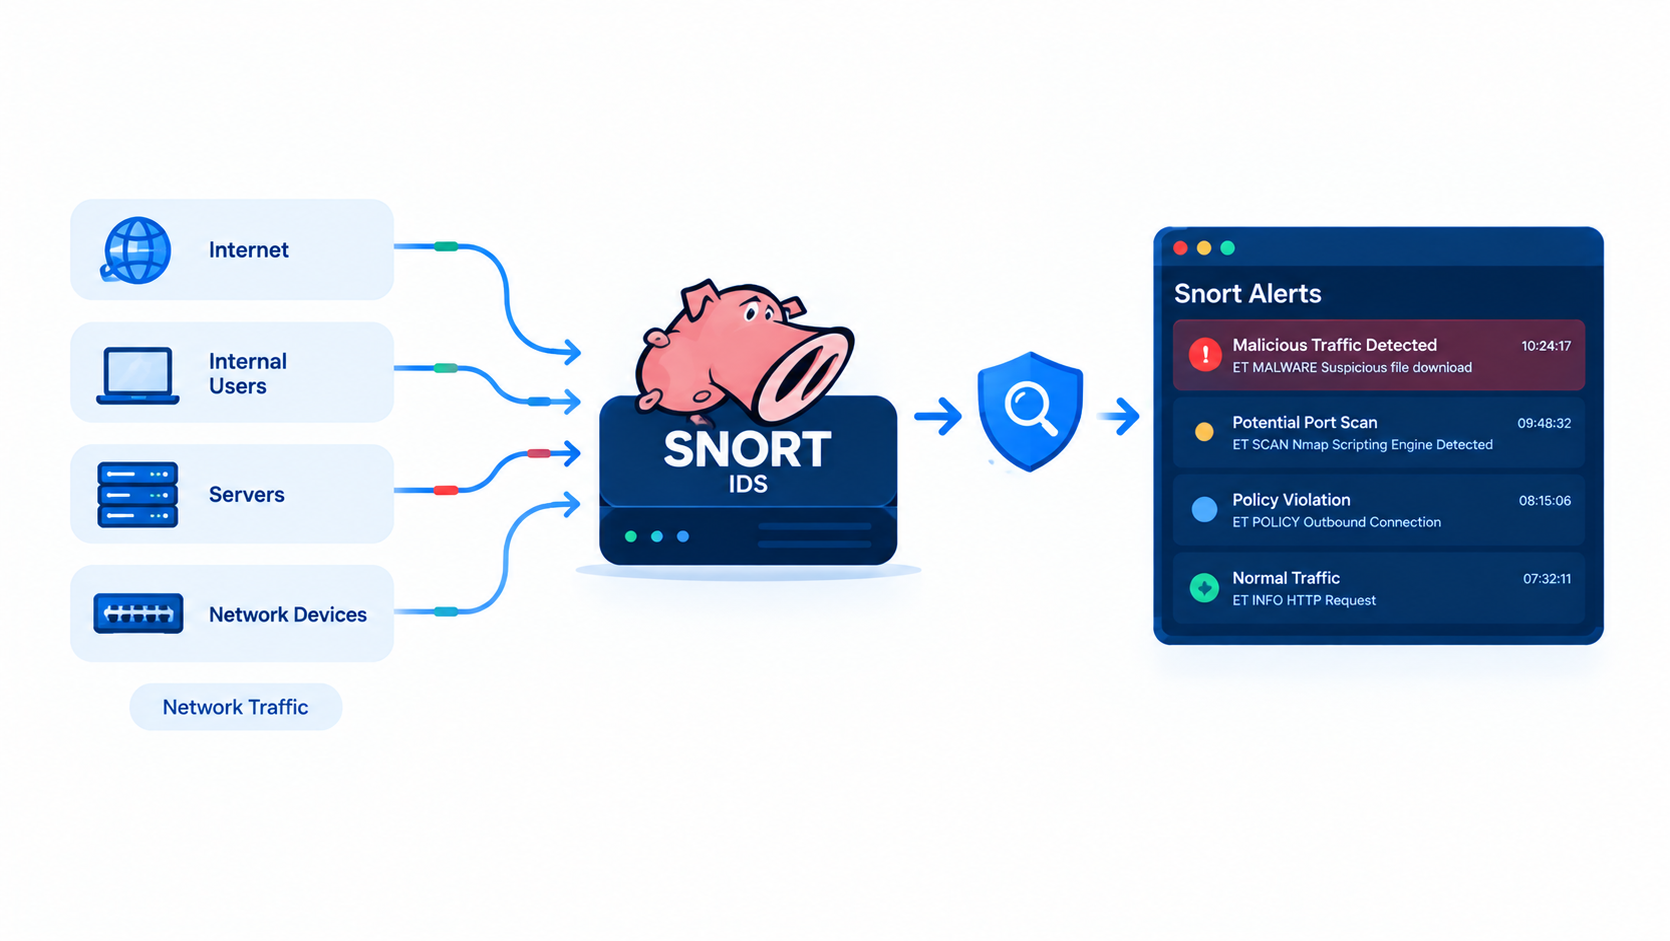
Attackers rarely knock before they enter. They scan your ports, guess your passwords, and probe your web apps, and every step leaves a trace on...
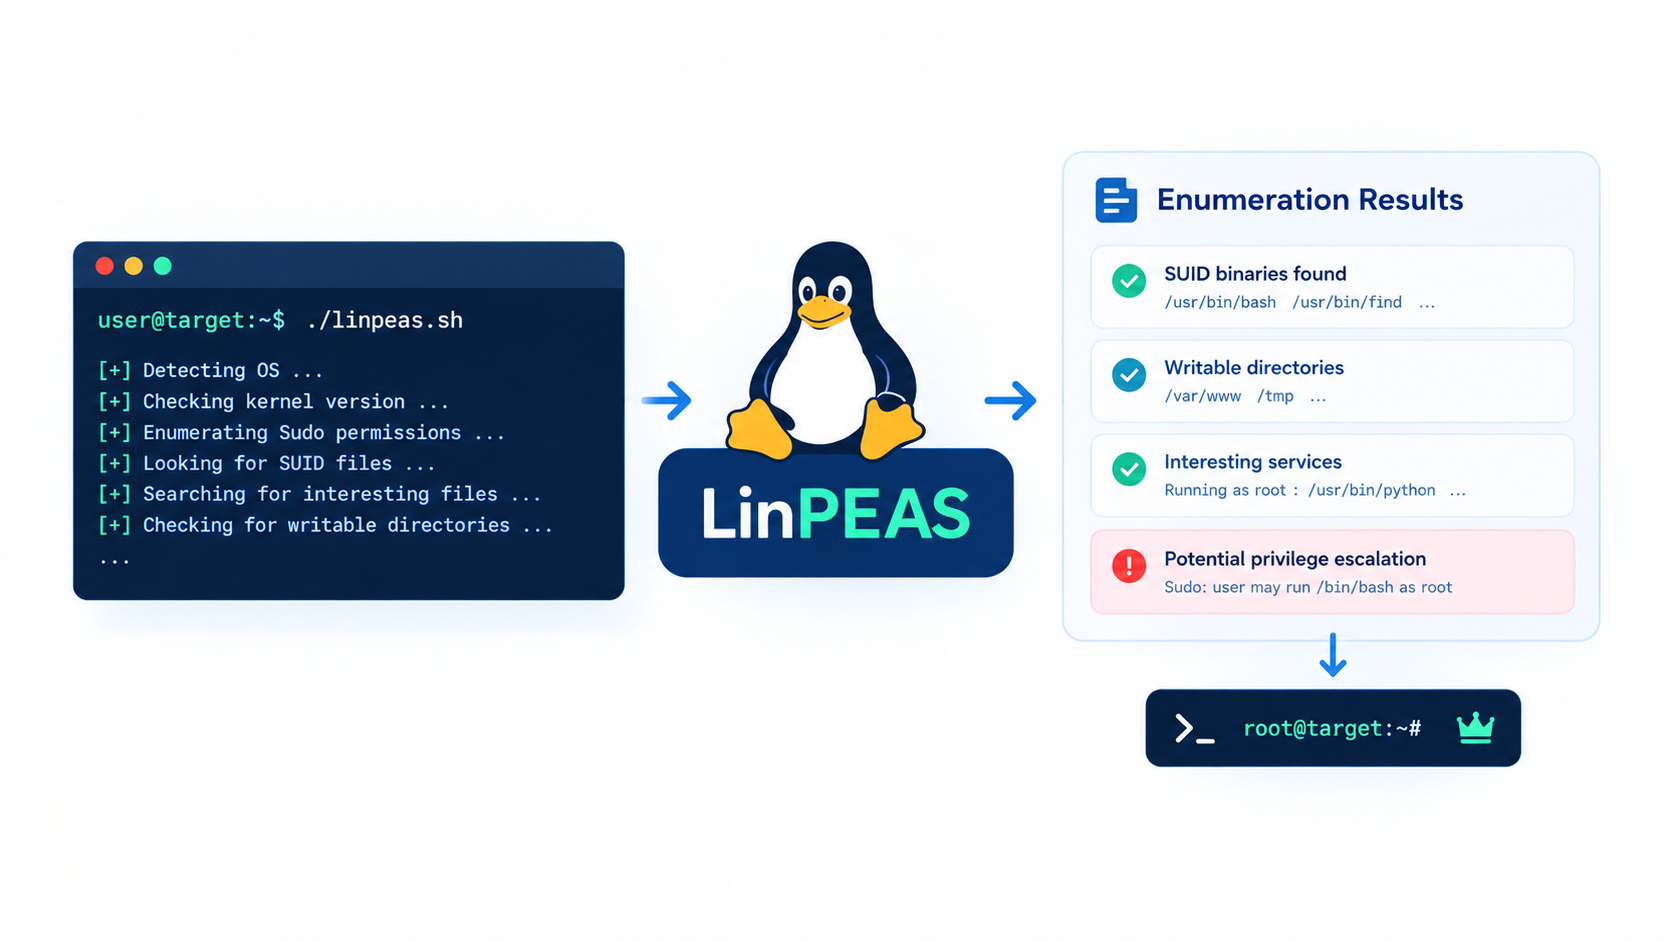
Every penetration tester reaches the same wall after gaining a low-privilege shell on a Linux box: now what? Manually checking permissions, cron jobs, and SUID...
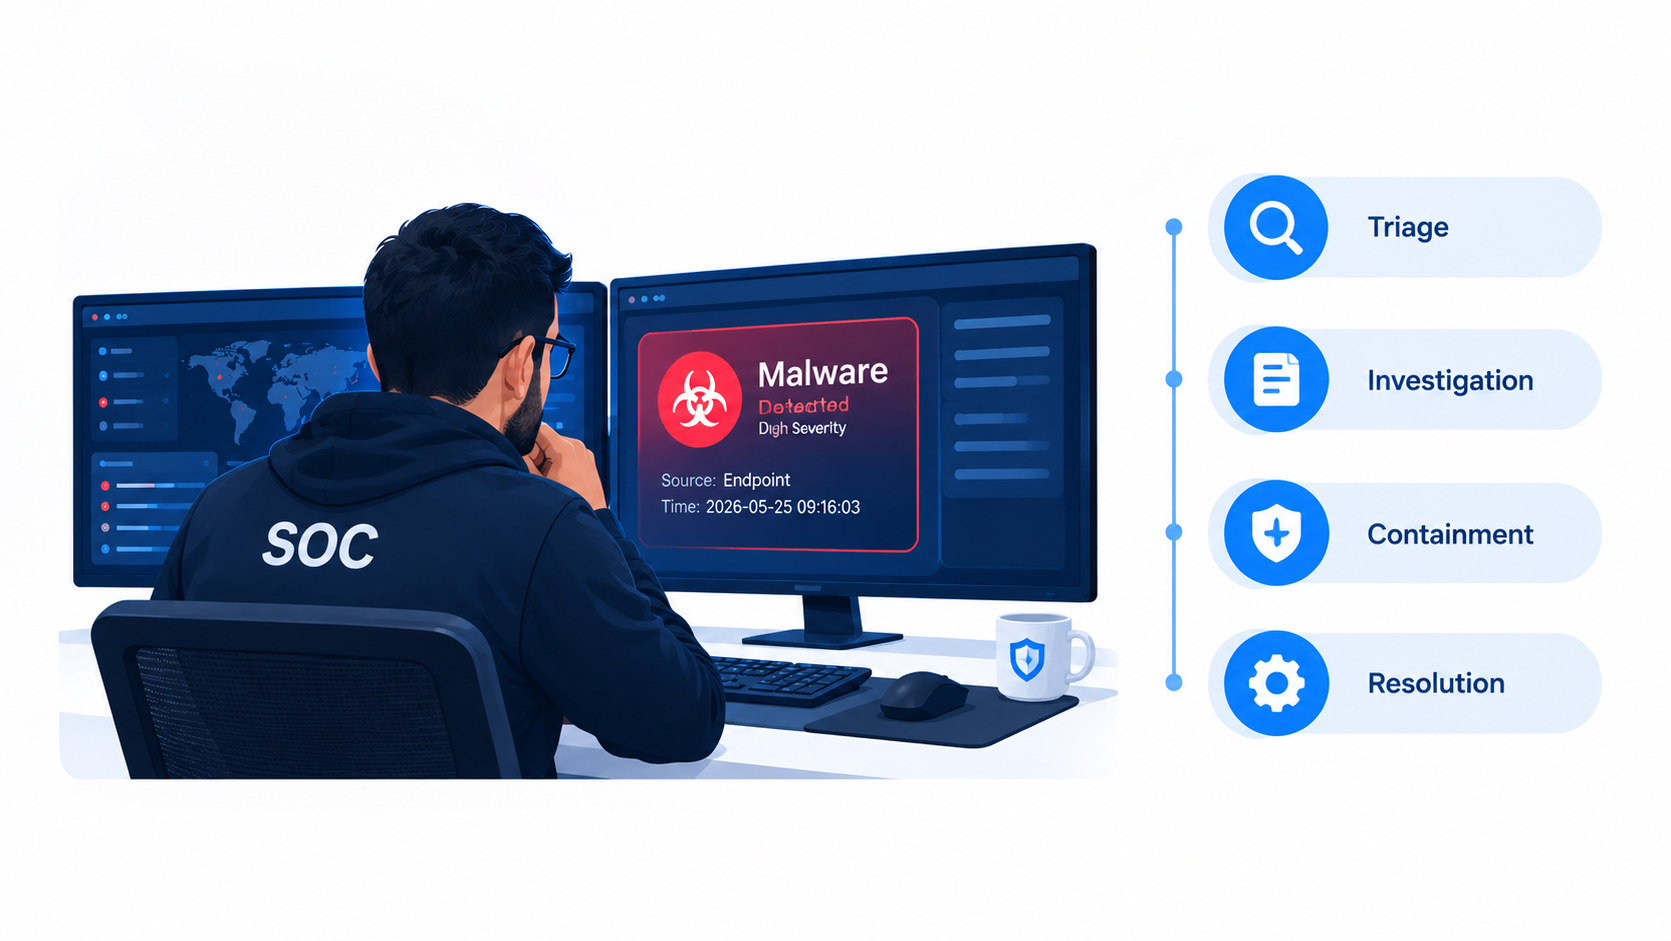
An alert pops up on the SOC dashboard: “Malware detected on WS-0142.” Within minutes, an analyst must decide whether it is a real attack or...
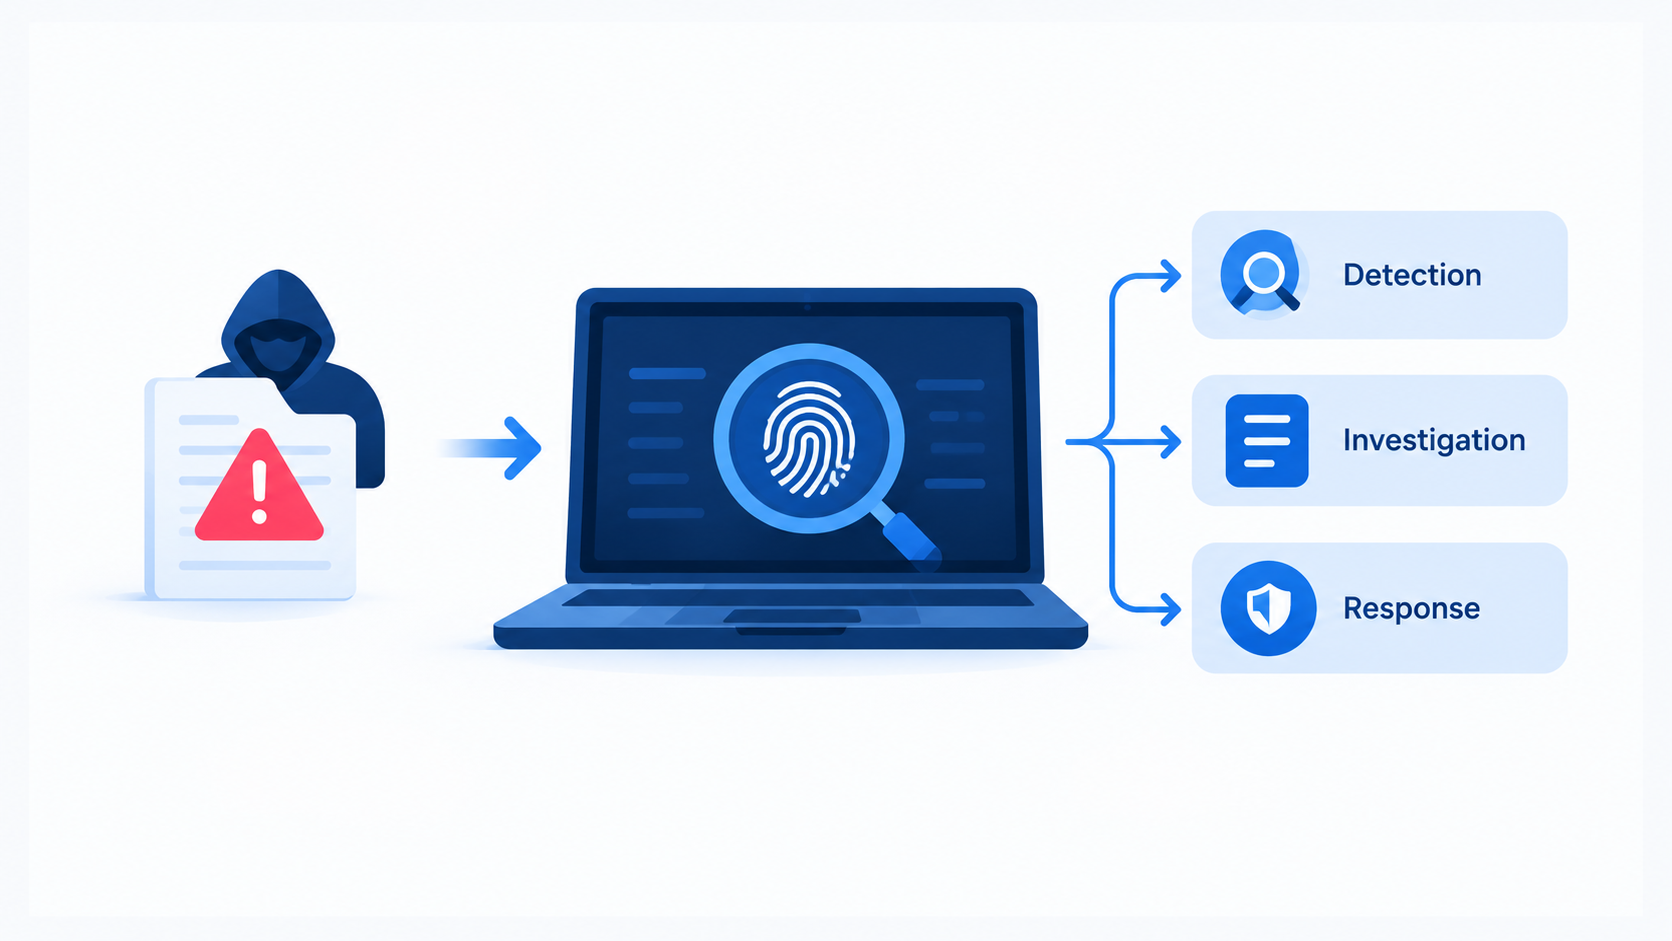
A ransomware note appears on a file server at 2 a.m. Someone must stop the spread. Someone else must find out how the attacker got...
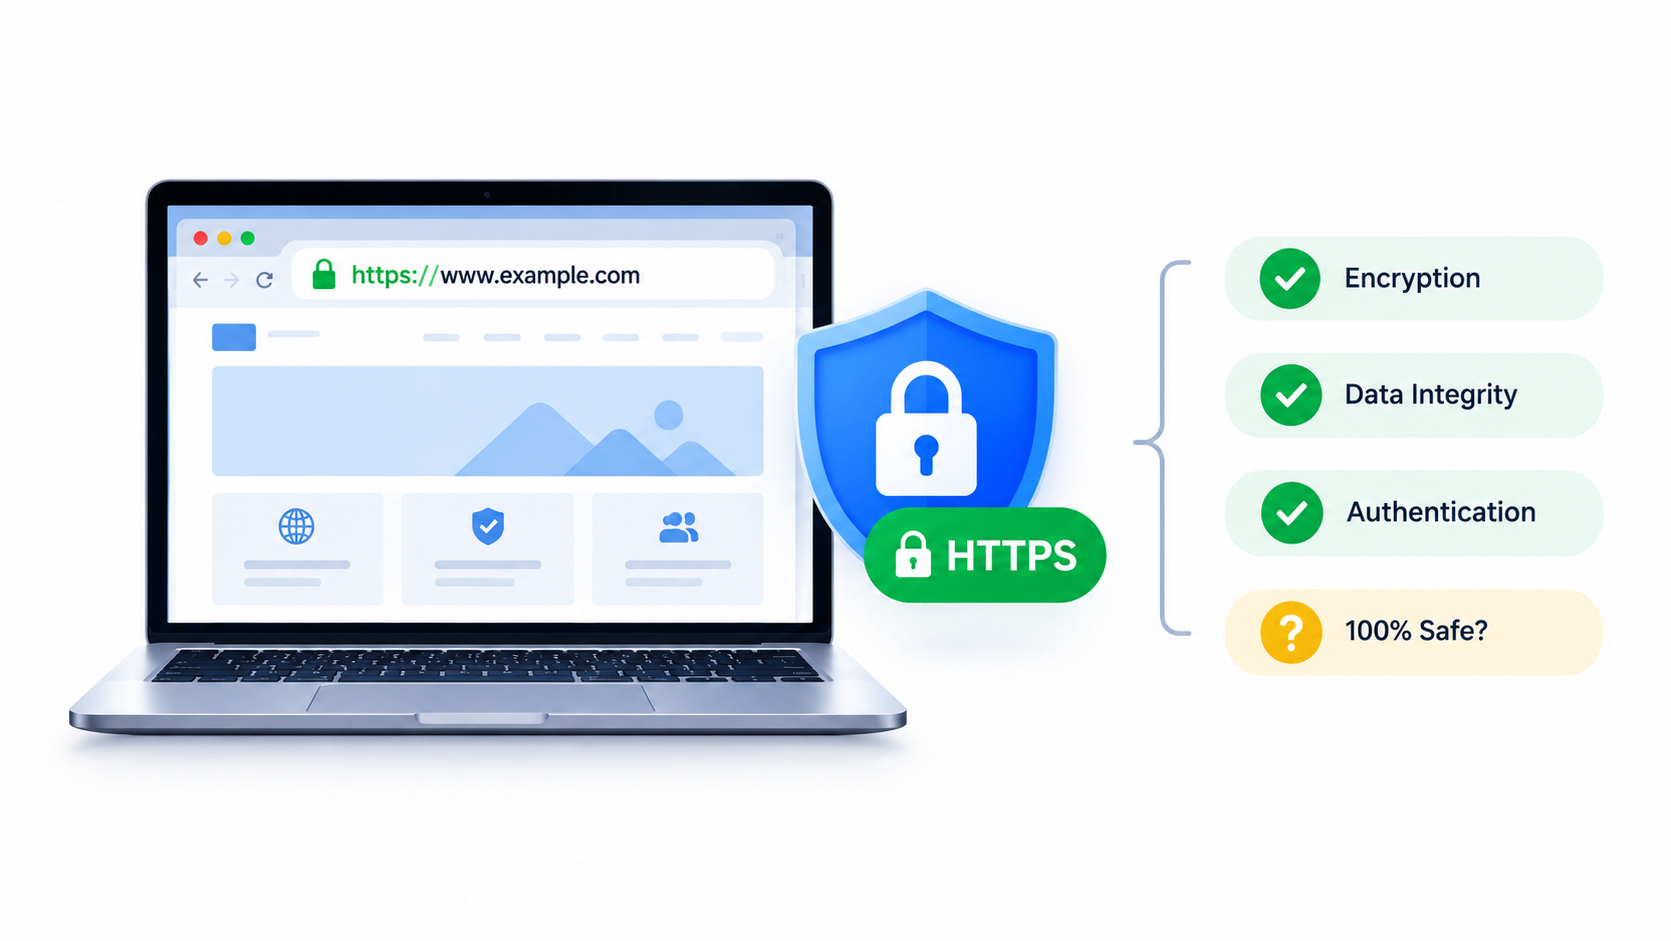
For years, security advice sounded simple: “Look for the padlock.” Browsers trained us to trust it. Attackers learned the same lesson and now put padlocks...